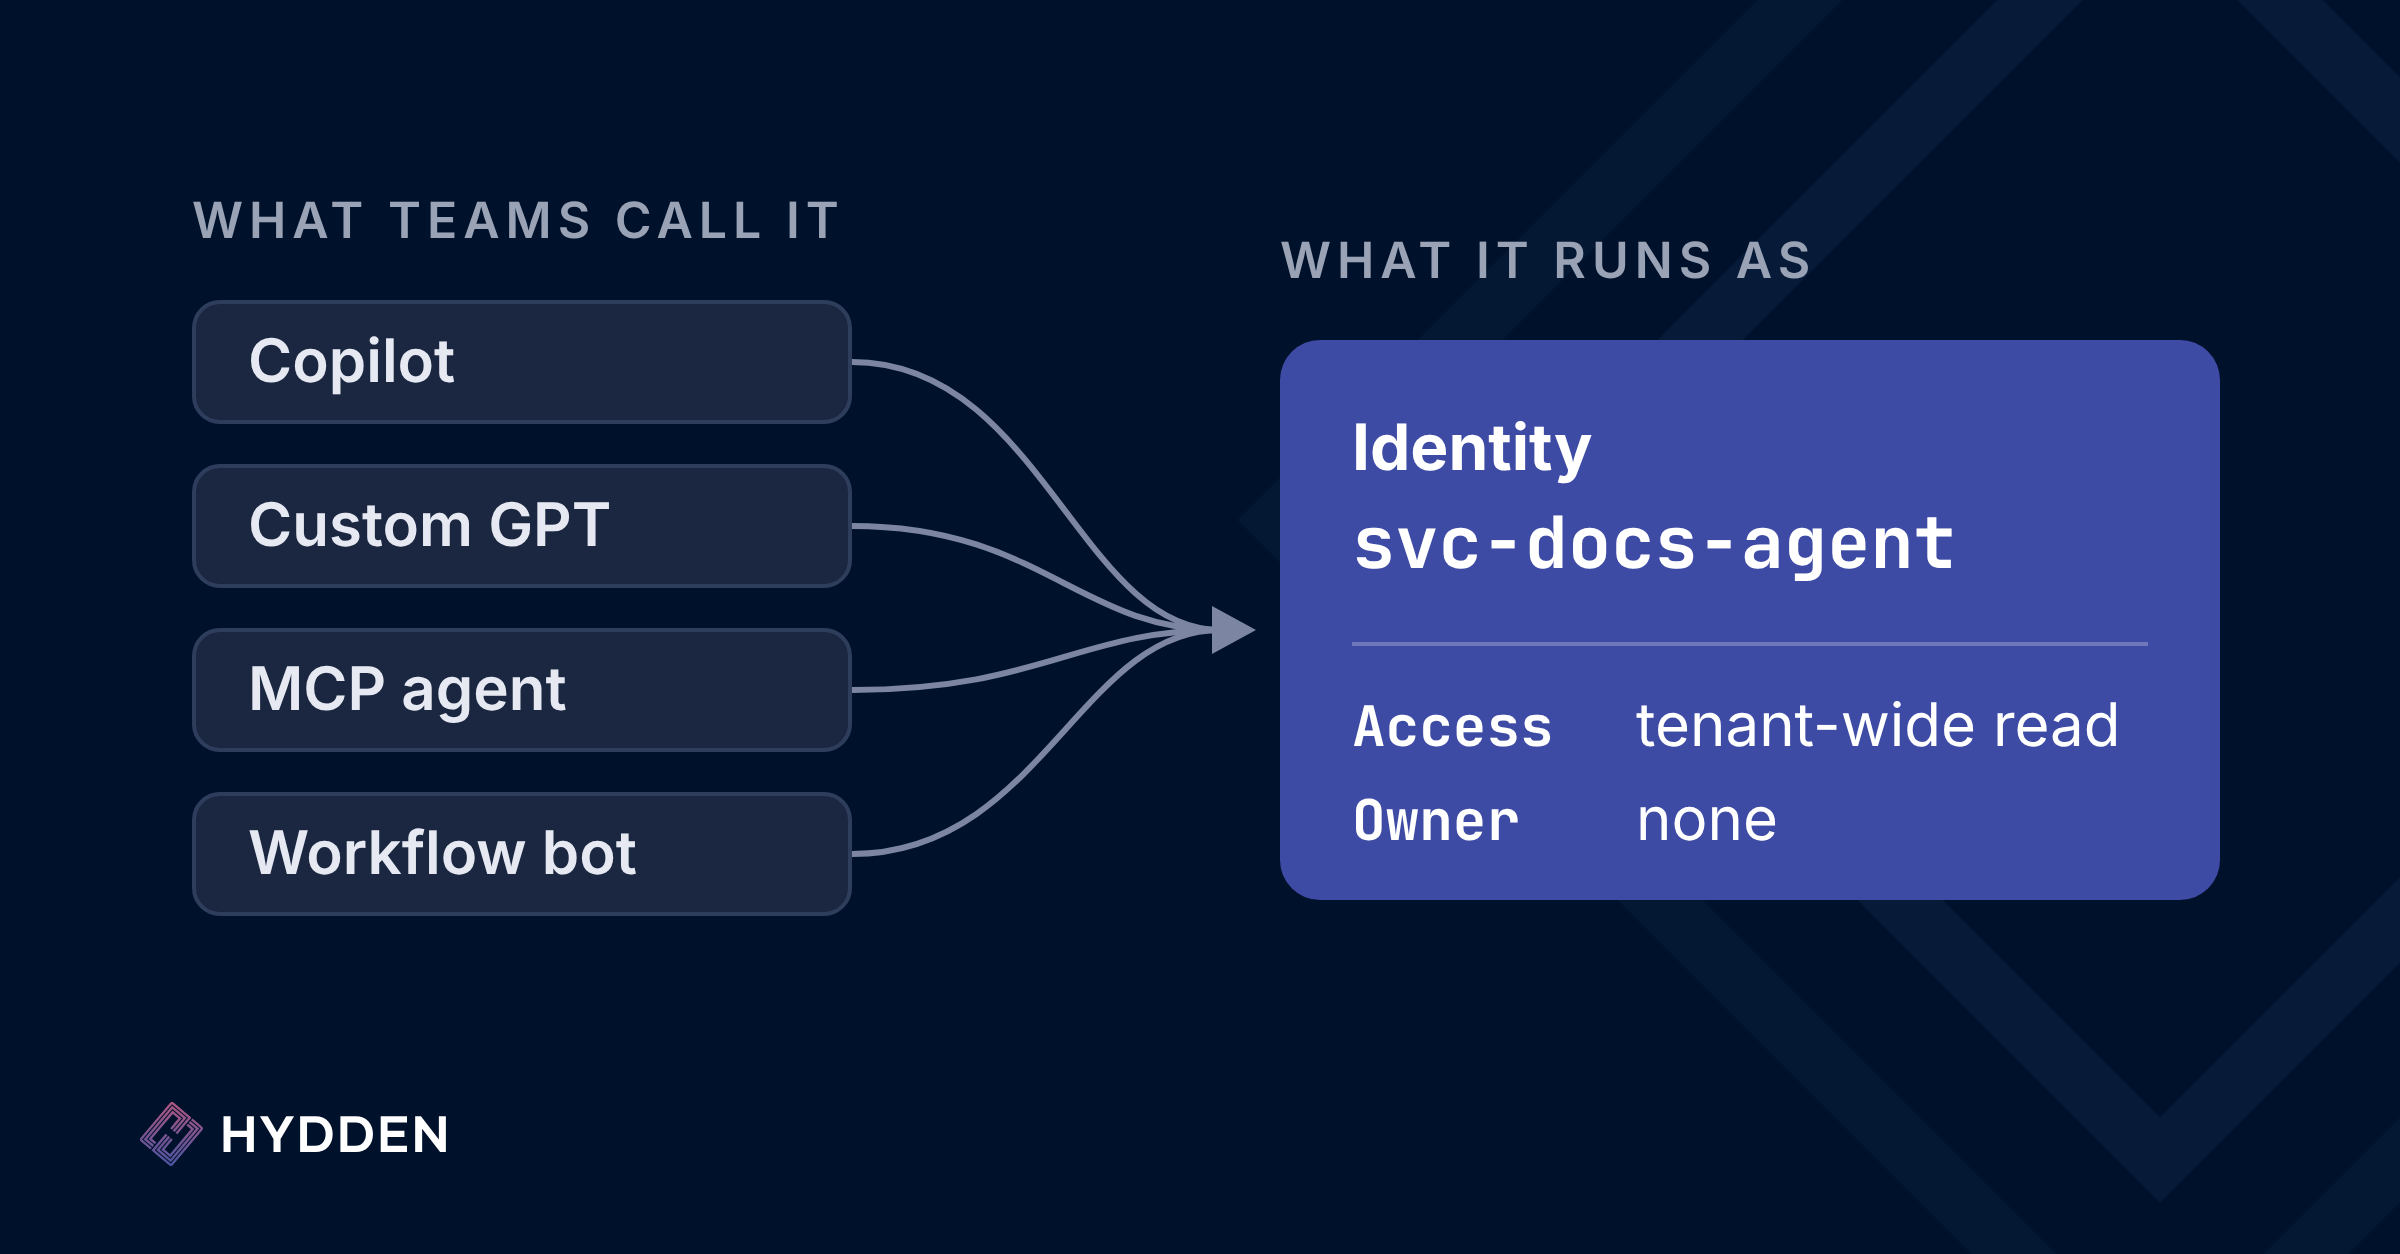
Ask what counts as an AI agent and every team gives a different answer. Copilots, custom GPTs, MCP-connected agents, workflow bots and agentic features inside SaaS apps all get the label, and the list keeps growing. That makes it hard for security teams to decide where to start.
Hydden starts from what they all have in common. Whatever you call it, an AI agent runs as an identity with access. That identity might be a dedicated service principal, a shared service account or a user's delegated token, and each of those is something you can inventory, assign an owner to and govern.
A familiar setup
A team wants an agent that answers questions from company documents. The developer building it registers an app in Entra ID and, to get it working quickly, grants it tenant-wide read access to SharePoint and OneDrive. The agent works, and nobody goes back to narrow the scope. When the developer later moves to another team, the agent keeps running with read access to every file in the tenant and no one responsible for it. Most security teams can't say how many agents like this they have or who owns each one.
The AI Agents view in Hydden Control, with each agent's platform and owner.
Lifecycle management isn't done yet
Joiner, mover and leaver processes for employees are still unfinished at most organizations. Movers are the usual weak spot, because a role change tends to add new access without removing the old. In a Cisco Duo survey of 680 IT and security leaders, 60% of CISOs said they lacked confidence in their joiner, mover and leaver process.
Governance for non-human identities is further behind. Service accounts, app registrations and API keys often sit outside IGA reviews and PAM vaults, and many have no named owner. AI agents run on the same kinds of accounts, so they inherit those gaps. An organization that hasn't finished lifecycle management for people, and is behind on service accounts, can't be close to ready for AI agents.
Start with one record
Governing agents starts with knowing which accounts they run as, what those accounts can reach, who owns them and how their access changed over time. That answer has to come from one record across every connected system, since an agent's account usually lives in one place while its access lands in several others.
Most identity tools learn about access by pulling periodic exports of current state. In those exports, the document agent's tenant-wide scope is one more line item. Nothing in it says when the scope was granted, who granted it, whether it went through an approval or that it was only meant to last until the agent was working. By the time an access review or an incident asks those questions, the developer who could answer them has moved to another team.
Hydden shows the path that grants an account its access, from account to role to permission to resource.
Where Hydden fits
Hydden is the identity security platform built on the Identity System of Record. It discovers accounts continuously across the systems you connect, including non-human identities and the accounts AI agents run as. Each change becomes a timestamped event, with the author wherever the source system captured it. Hydden links each account to the person responsible for it, flags accounts left without an owner and shows which accounts hold privileged access. When the developer in the example changes teams, the agent's account shows up with no owner, along with what it can reach and how that access changed.
Blast radius shows everything an account can reach. This one reaches 99 connected nodes across three hops.
Agent Studio lets teams automate the response from triggers and actions. It can route the finding to the right manager to assign a new owner and, once a person approves, ask the system that owns the access to remove what the agent no longer needs. Hydden verifies the result and records each step, while the change itself happens in your existing systems.
Request a trial to see which accounts your AI agents run as and who owns them.